Editable toolkits for the risk analysis, policies, incident response and vendor tracking that OCR asks for first, built by a healthcare IT Director with 20+ years running hospital and clinic technology.
Get the free readiness checklistSee the toolkitsHIPAA's Security Rule expects every covered entity to have a current risk analysis, written policies, and evidence that it acted on what it found. Missing or superficial risk analyses are among the most common problems in OCR enforcement.
It is the first document OCR requests after a breach report or complaint. "Our IT company handles it" is not an answer.
Generic policies that don't match your systems are easy to spot and hard to defend.
Ransomware, a lost laptop or a misdirected email each start a breach-notification clock. A tested plan saves days.
Instant download. Word and Excel files you can edit and keep. Licensed for one organization.
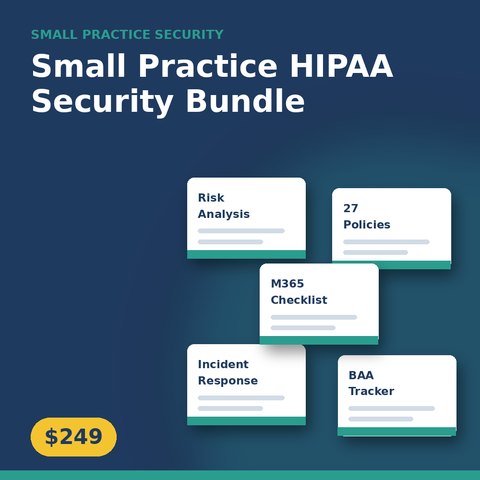
All five toolkits: risk analysis workbook, 27 policies, incident response kit, vendor/BAA tracker and Microsoft 365 checklist.
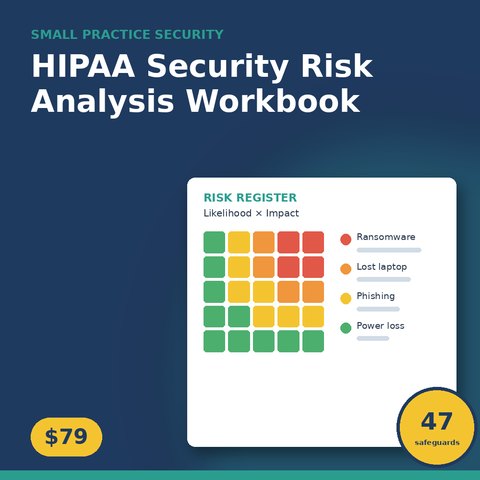
Excel workbook with 30-threat library, all 47 Security Rule specifications, auto-scored risk register, remediation plan, and a step-by-step guide.
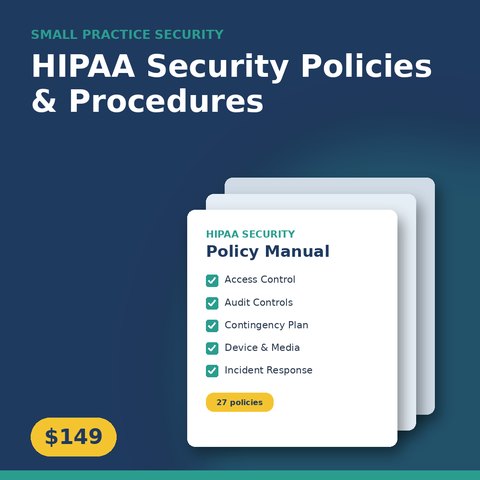
27 editable Word policies mapped to the Security Rule, plus adoption memo and workforce acknowledgment forms.
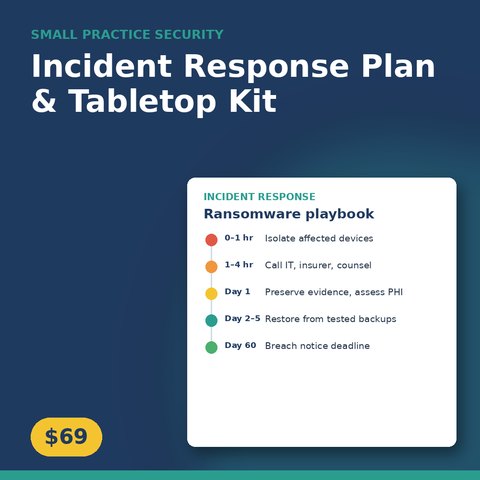
IR plan, five playbooks (ransomware, lost device, misdirected email, vendor breach, insider), and a ready-to-run tabletop exercise.
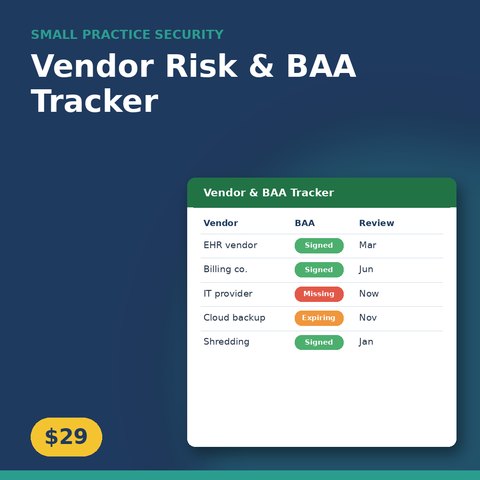
Track every vendor that touches ePHI, BAA status and review dates, with a BAA checklist and vendor security questionnaire.
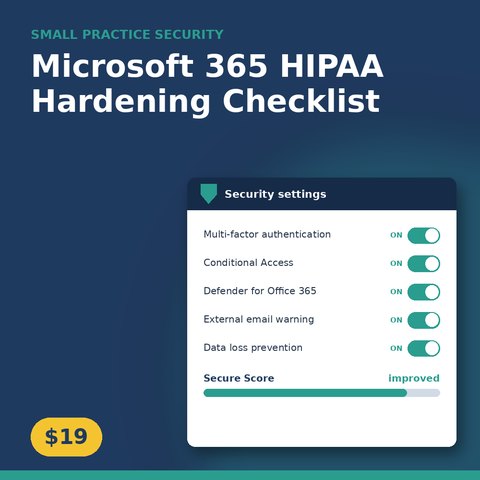
32 Microsoft 365 settings that matter for ePHI, each mapped to the HIPAA safeguard it supports.
The same practical approach for any small business: a cyber risk assessment mapped to NIST CSF 2.0, 21 security policies, an incident response and ransomware kit, and cyber insurance readiness.
See the cyber toolkitsPlain-English answers to the questions practice managers ask most.
Fixed-price help from a healthcare IT Director with 20+ years running technology and security for hospitals and clinics.
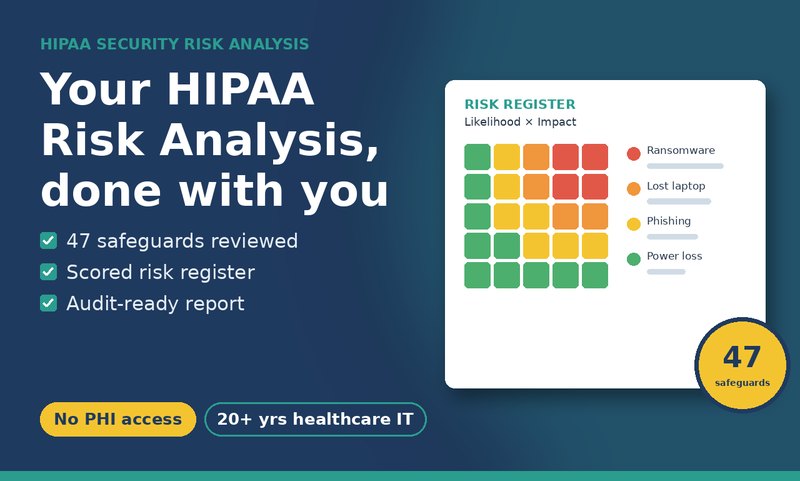
Done with you: asset inventory, all 47 safeguards reviewed, scored risk register and an audit-ready written report.
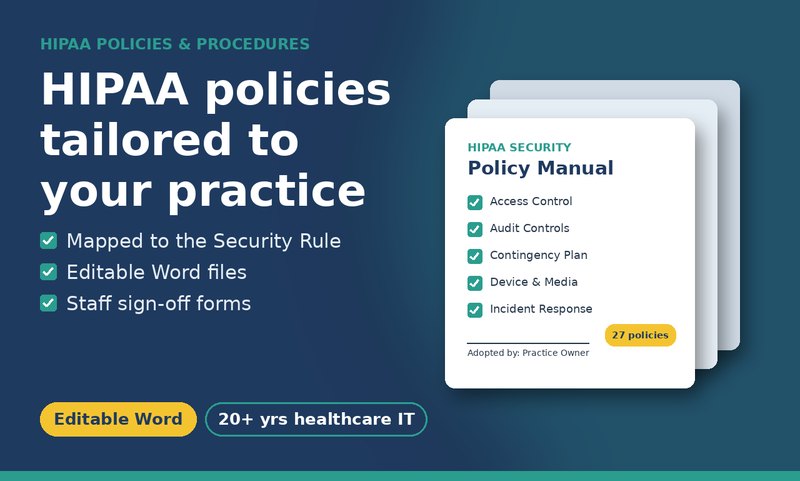
Security Rule policies edited for your systems and staff, with adoption and sign-off forms.
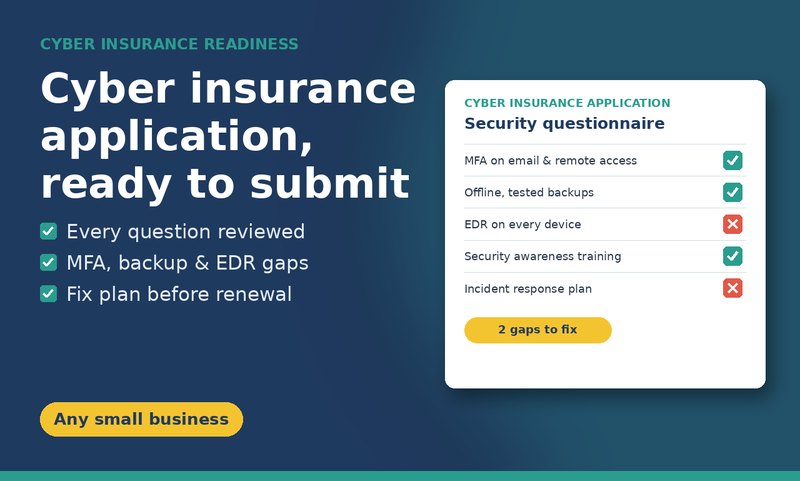
Every insurer question checked, MFA, backup and EDR gaps flagged, and a fix plan before you submit. Any small business.
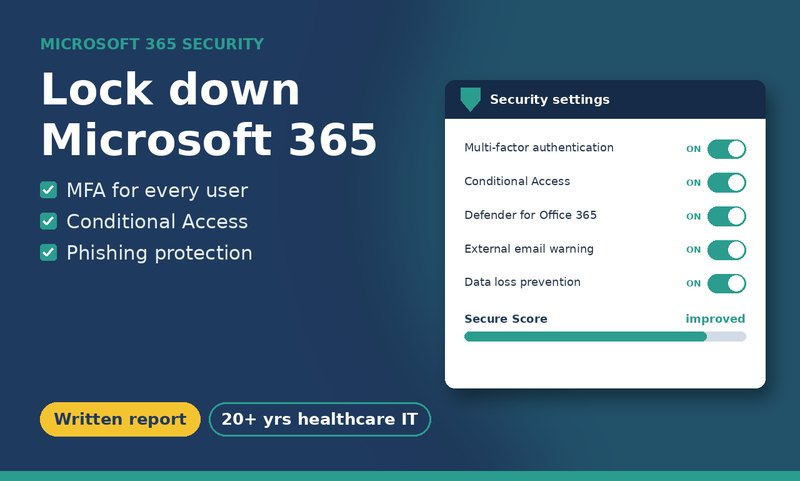
MFA for every user, Conditional Access, phishing protection and a written audit report.
Questions first? Email support@smallpracticesecurity.com with your number of locations and staff. Fully remote; no access to patient data needed.